
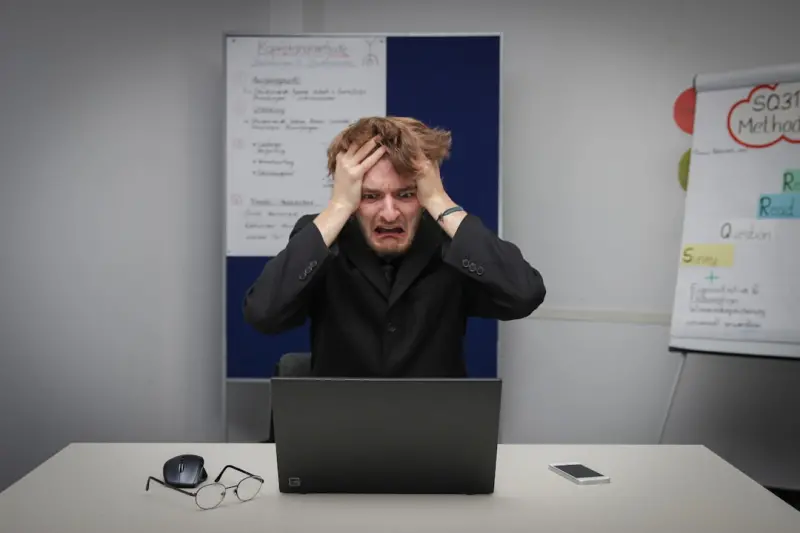
Online safety isn’t just about firewalls, encryption keys, or the latest security patch. It’s an evolving conversation between technology, human behavior, and the subtle ways our brains get worn down by constant threat alerts. In the last few years, the sheer volume of phishing attempts, deep‑fake videos, and credential‑stuffing attacks has turned what used to be an occasional “got‑cha” moment into a relentless background hum. That hum—what I like to call phishing fatigue—drains cognitive bandwidth, lowers vigilance, and ultimately creates the very vulnerabilities attackers are hunting.
The Anatomy of Phishing Fatigue
Imagine your inbox as a revolving door. Every hour, dozens of messages slip through, each promising a prize, a warning, or a request for urgent action. Your brain, wired to prioritize novelty and potential loss, fires an alarm each time. But after the 50th alert, the signal‑to‑noise ratio collapses. The mental shortcut shifts from “stop and verify” to “just ignore.” Studies in cognitive psychology show that repeated exposure to low‑stakes threats reduces the amygdala’s response, making us desensitized to real danger. In the corporate world, this means a security‑aware employee can become an inadvertent gateway for a breach simply because they stopped paying attention.
Why Traditional Security Messaging Misses the Mark
Most security programs still rely on a “one‑size‑fits‑all” approach: monthly newsletters, quarterly training videos, and generic pop‑ups that say “Don’t click suspicious links.” While well‑intentioned, these tactics treat safety as a static checklist rather than a dynamic mental habit. They ignore two crucial facts:
- Context matters. A sales rep closing a deal in a coffee shop faces different risks than a developer pushing code from a home office.
- Emotion drives action. Fear‑based warnings can backfire, causing users to shut down or, worse, to over‑react and click “allow” on the wrong prompt just to silence the alarm.
When the message itself becomes another source of noise, it contributes to the fatigue cycle instead of breaking it.
Designing Safety for the Human Brain
To reclaim attention, safety communications must align with how our brains actually process risk. Here are three design principles that have proven effective in pilot programs across tech‑forward enterprises:
- Micro‑learning bursts. Instead of a 30‑minute video, deliver 60‑second “security snack” clips that focus on a single, actionable tip. The brevity respects limited attention spans while reinforcing one behavior at a time.
- Contextual nudges. Embed prompts directly into the tools people use—email clients, collaboration platforms, and even IDEs. A subtle banner that appears only when a user is about to paste a credential into an unfamiliar domain is far more impactful than a generic email.
- Positive reinforcement. Celebrate safe behavior with visible, low‑stakes rewards (badges, shout‑outs, or small gift cards). Recognition taps into the brain’s dopamine pathways, making the safe choice feel rewarding rather than burdensome.
From Devices to Desks: Future‑Proofing Your Tech Stack
Security fatigue is amplified when devices themselves feel insecure. Outdated operating systems, unpatched firmware, and clunky security suites add friction that users work around—often by disabling protections. The future‑proofing your devices playbook emphasizes a proactive refresh cycle, standardized image deployment, and zero‑trust networking. By ensuring that every laptop, tablet, and peripheral runs the latest baseline, you eliminate a major source of user‑driven workarounds and keep the focus on thoughtful, intentional actions.
The Role of Mobile Apps in Reducing Fatigue
Mobile workforces are especially vulnerable. Push notifications from corporate apps can become a double‑edged sword: they keep teams informed but also add to the alert overload. The solution isn’t less communication; it’s smarter communication. Designing apps with a playful mobile security mindset—think gamified risk assessments, interactive “what‑if” scenarios, and visual threat dashboards—transforms routine checks into engaging experiences. When users look forward to a quick, interactive safety check, the cognitive load drops dramatically.
Deepfakes: The Next Frontier of Social Engineering
Phishing isn’t limited to text. Deepfake audio and video have entered the corporate threat landscape, allowing attackers to impersonate CEOs in real‑time video calls. Because visual and auditory cues are powerful trust signals, a well‑crafted deepfake can bypass many of the heuristics employees rely on. Combatting this requires both technological and behavioral defenses:
- Verification protocols. Institute a simple, universal phrase (“Blue Tiger 42”) that must be spoken at the start of any high‑value request, regardless of the medium.
- AI‑driven detection. Deploy tools that scan inbound video streams for inconsistencies in lighting, lip‑sync, and facial micro‑expressions.
- Human rehearsal. Run mock deepfake drills during team meetings to build instinctive skepticism.
Balancing Transparency and Privacy
When you push more security data to users—like risk scores on emails or real‑time threat maps—you risk crossing the line into privacy invasion. Employees should never feel they’re being monitored like a CCTV feed. Transparency about what data is collected, why it’s needed, and how it’s stored is essential. Provide an easy‑to‑access dashboard where users can see their own activity logs and opt‑out of non‑essential telemetry. This openness builds trust, which in turn fuels higher engagement with safety protocols.
Psychological First Aid for Security Teams
Security teams themselves experience fatigue. Constantly triaging alerts, dealing with false positives, and watching a breach unfold can lead to burnout—a hidden cost that ripples out to the entire organization. Implementing psychological first aid (PFA) practices helps mitigate this:
- Debriefing sessions. After a major incident, hold a no‑blame review that focuses on lessons learned and emotional processing.
- Rotating on‑call duties. Avoid long stretches of high‑stress monitoring by rotating staff and providing “quiet” days.
- Access to counseling. Partner with mental‑health providers who specialize in tech‑stress to offer confidential support.
Measuring Success Beyond Click‑Rates
Traditional metrics like phishing‑simulation click‑through rates are useful but incomplete. To truly gauge fatigue reduction, broaden your KPI set:
- Alert fatigue index. Track the average number of security alerts a user receives daily versus the number they acknowledge.
- Engagement quality. Measure time spent on micro‑learning modules, not just completion rates.
- Incident resolution time. Faster, more confident responses indicate a healthier security mindset.
When these metrics move in the right direction, you know you’ve shifted from a reactive “catch‑the‑phish” model to a proactive “mindful‑security” culture.
Building a Culture of Safe Curiosity
People are naturally curious. They’ll test a link, explore a new tool, or share a meme—sometimes at the edge of policy. Instead of policing curiosity, channel it. Create a “sandbox” environment where employees can safely experiment with unfamiliar URLs, third‑party apps, or new collaboration features. Offer a badge for reporting a false positive discovered in the sandbox. This approach turns potential risk‑taking into a structured learning opportunity, reinforcing the idea that safety is a shared, exploratory journey.
Action Plan: 7‑Step Playbook to Defeat Phishing Fatigue
- Audit alert frequency. Identify which channels (email, Slack, mobile) are over‑communicating.
- Segment audiences. Tailor messages to roles—sales, engineering, finance—so relevance spikes.
- Implement micro‑learning. Deploy daily 30‑second tips via a dedicated security channel.
- Introduce contextual nudges. Use real‑time prompts that appear only when risky behavior is detected.
- Gamify safe actions. Award points for completing verification steps, redeemable for perks.
- Run deepfake drills. Simulate video‑call scams quarterly to keep detection skills sharp.
- Review and iterate. Quarterly, analyze the alert fatigue index and adjust frequency, tone, and format.
Following this roadmap not only reduces fatigue but also cultivates a security‑savvy workforce that feels empowered rather than burdened.
Looking Ahead: The Human‑Centric Future of Online Safety
As AI assistants become commonplace and the line between work and personal digital life blurs, the definition of “online safety” will expand. It won’t be just about preventing data loss; it will be about safeguarding mental bandwidth, emotional well‑being, and the trust that underpins every digital interaction. By designing safety systems that respect cognitive limits, celebrate correct behavior, and provide psychological support, organizations can turn the tide on phishing fatigue and build a resilient, human‑first security culture.
Amanda is a passionate writer exploring a kaleidoscope of topics from lifestyle to travel and everything in between.
Related Posts

Beyond the Password: A Human‑First Playbook for Online Safety
A human‑first approach to online safety goes beyond passwords, tackling AI‑driven phishing, deep... Read More

How to Defend Your Digital Identity from Deepfake Threats
Discover actionable steps to safeguard your digital identity against deepfake attacks, from footprin... Read More
Navigating Online Safety in 2026: A Sustainable, Human‑Centric Playbook
A 2026 roadmap to online safety that merges eco‑friendly tech, AI threat awareness, and community ... Read More
Top Posts

Celebrating the Small: How Everyday Wins Turn Into Meaningful Rituals
Learn to turn everyday achievements into meaningful rituals with inclusive, eco‑friendly, and tech‑enhanced celebrations that boost joy and community spirit...Read More

The Hidden Economics of Hyper‑Personalized Shopping: Data, Delight, and Dilemmas
A deep dive into the data‑driven world of hyper‑personalized shopping, uncovering the economic benefits, privacy concerns, and practical strategies for reta...Read More
Kids Safety in the Age of Sustainability: A Parent’s Playbook
Explore how green choices—from toys to tech—can boost child safety, offering parents a sustainable playbook for protecting the next generation....Read More
Career Resilience: Turning Setbacks Into Strategic Momentum
Learn to convert career setbacks into growth opportunities through resilience, data‑driven reflection, mentorship, and storytelling—turn challenges into you...Read More
0 Comments
Post Comment
You will need to Login or Register to comment on this post!